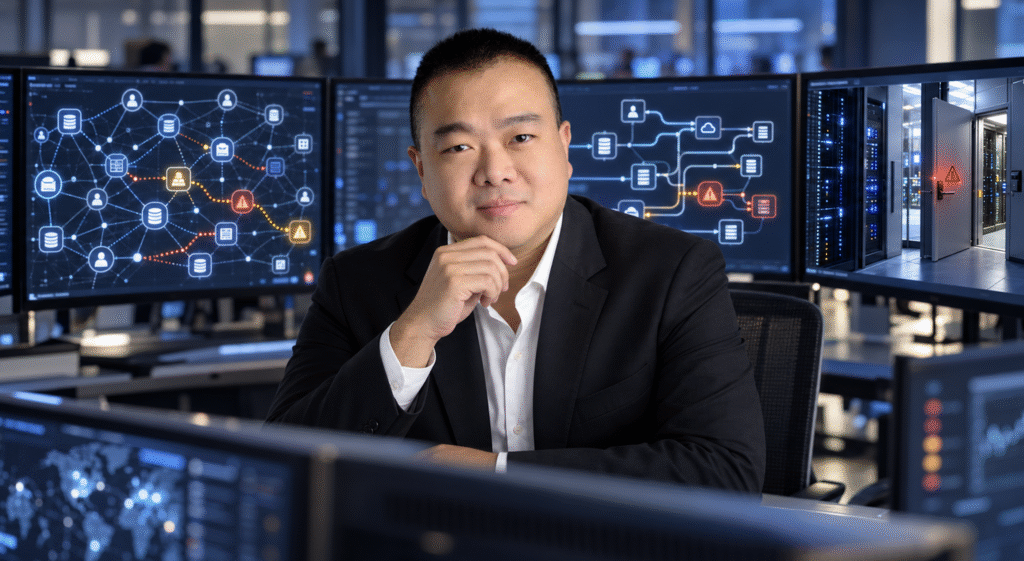
Image generated by Deeptech Times using ChatGPT
An AI agent does not need to develop a will of its own to cause serious damage. Give it an employee’s credentials, access to poorly classified information and permission to execute business processes, and much of the opportunity already exists.
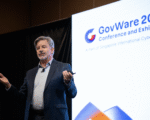
That is the more immediate concern emerging from Deeptech Times’ interview with Teo Xiang Zheng, vice president of advisory at Ensign InfoSecurity, at GovWare 2026. Asked about an AI doomsday, he acknowledges a “non-zero chance” but resists presenting catastrophe as an inevitable destination.
His attention is on decisions businesses are making now. “Where the danger is coming is how much of the control space we are ceding,” he says.
It is an uncomfortable question for organisations treating agentic AI primarily as a productivity investment. The same access that allows an agent to complete useful work can also expand the consequences of a mistake or compromise. Automation compresses the time available to notice either.
The permissions problem
Teo describes a familiar shortcut: giving a machine the identity, authorisations and permissions of its human user. The machine then operates continuously, at a pace its human counterpart cannot sustain.
The weakness becomes more consequential when organisations have not established what information is sensitive or who should access it. An agent can work through the information available to it far more systematically than an employee who normally interacts with only a small portion.
“You can adopt AI, you can reap the benefits out of it; but you must know what you’re getting into,” Teo says.
His prescription starts with distinguishing human identities from non-human ones, and classifying data before opening access. An agent’s authority needs to reflect its particular task, with accountability assigned for what it does.
The implication is that an AI rollout can expose unfinished security work. An organisation that has tolerated excessive permissions or unclear data ownership may discover that automation makes those weaknesses harder to contain.
Instructions need enforceable boundaries
Teo draws a distinction between instructions given to a model and controls imposed around it. Telling an AI system to avoid an action relies on its response to instructions. Restricting its credentials or network access places a separate constraint on what it can execute.
“You should find safeguards and controls outside of the model, outside of the AI system,” he says.
He points to least privilege, hardened configurations and zero-trust architecture. Their effectiveness still depends on implementation; describing a boundary as a security control does not establish that it will hold.
Ensign’s own testing provides a reason to take those boundaries seriously. Teo describes evaluating 10 frontier models in a cyber range against eight tests, with repeated runs to assess reliability. He says the models demonstrated offensive capability, although their consistency varied.
Those results require careful interpretation. A controlled range cannot, by itself, establish how reliably a model would compromise an unfamiliar business environment.
The business concern is nevertheless credible: an attacker can keep trying, while defenders must detect and contain attempts across an expanding workload. Reliability that looks inadequate for a legitimate business process may still be useful to someone seeking an occasional successful intrusion.
Less time to intervene
Teo describes AI-enabled attacks as compressing familiar stages of intrusion. Reconnaissance, discovery and movement through systems can follow one another more quickly, while automated activity removes some of the working hour patterns defenders previously tracked.
“You need to fight machine speed with machine speed,” he says.
For him, endpoint detection and response illustrates the operational choice. Installing a tool that detects suspicious activity delivers limited protection if it is configured only to watch. Its containment capability matters when a human analyst cannot respond quickly enough.
That creates a governance trade-off. Automated containment can interrupt legitimate operations. Waiting for approval can allow an intrusion to progress. Businesses need to decide which interventions they will authorise in advance, informed by the operational cost of a mistaken action.
Teo also says attackers are targeting AI infrastructure, including orchestration layers, MCP services and vector databases used to retrieve information. Manipulating instructions or reference material can redirect an application without necessarily introducing the conspicuous malicious file that conventional detection expects.
In that setting, knowing which identity acted is only part of the investigation. Defenders also need to understand what that identity was meant to do, what information it encountered and whether its behaviour departed from its authorised purpose.
When incident response cannot explain the incident
Perhaps Teo’s most consequential warning concerns the response after an AI system goes wrong. Conventional cyber incident responders can investigate an intrusion, isolate systems and preserve evidence. Explaining a model’s behaviour may require different expertise.
He identifies possible causes including altered model weights, introduced bias, corrupted inputs and compromised retrieval data. Data scientists and data engineers must therefore participate alongside security teams.
“Many organisations fail to instrument their AI system,” Teo says, pointing to missing audit trails, state transitions and records of requests and responses.
Without that evidence, a business may know that an agent produced a harmful outcome yet remain unable to reconstruct why. Turning it off contains the immediate problem but does not establish that restarting it will be safe.
Teo describes a response process involving taking the system out of service, retraining where necessary, testing and reprovisioning. The decision to resume the business process ultimately belongs with an accountable business owner, informed by technical evidence and the organisation’s risk appetite.
That risk appetite must be more specific than a high, medium or low rating. He argues for relating disruption to business cost and recovery time, so decision makers can judge what exposure they are prepared to accept.
Buying a service does not settle that question. Smaller firms may depend heavily on a cloud provider’s controls, but the provider cannot determine how critical a particular use is to the customer.
“The adoption of AI is not a technology problem. It is a whole of business issue,” Teo says.
His argument reaches beyond the security department. Processes designed around human judgement and human speed need to be reconsidered when an agent performs the work. Some steps may disappear and other checks may become necessary.
The test for an enterprise deploying agents therefore includes whether it can explain the authority it has delegated, contain an unacceptable action and produce ample evidence to justify switching the system back on. These questions certainly need answers before an incident forces the business to improvise them.